no tech sales
Most security consulting firms get a cut of the tools they convince you to buy. We don't. You won't get a garbage product recommendation because it nets us 6 points in margin.
// about simple salt
Simple Salt was founded in 2024 by Dylan Evans on a simple premise: replace audit-driven security with data-backed threat assessments that show what truly puts a business at risk — and what leaders can safely stop paying for.
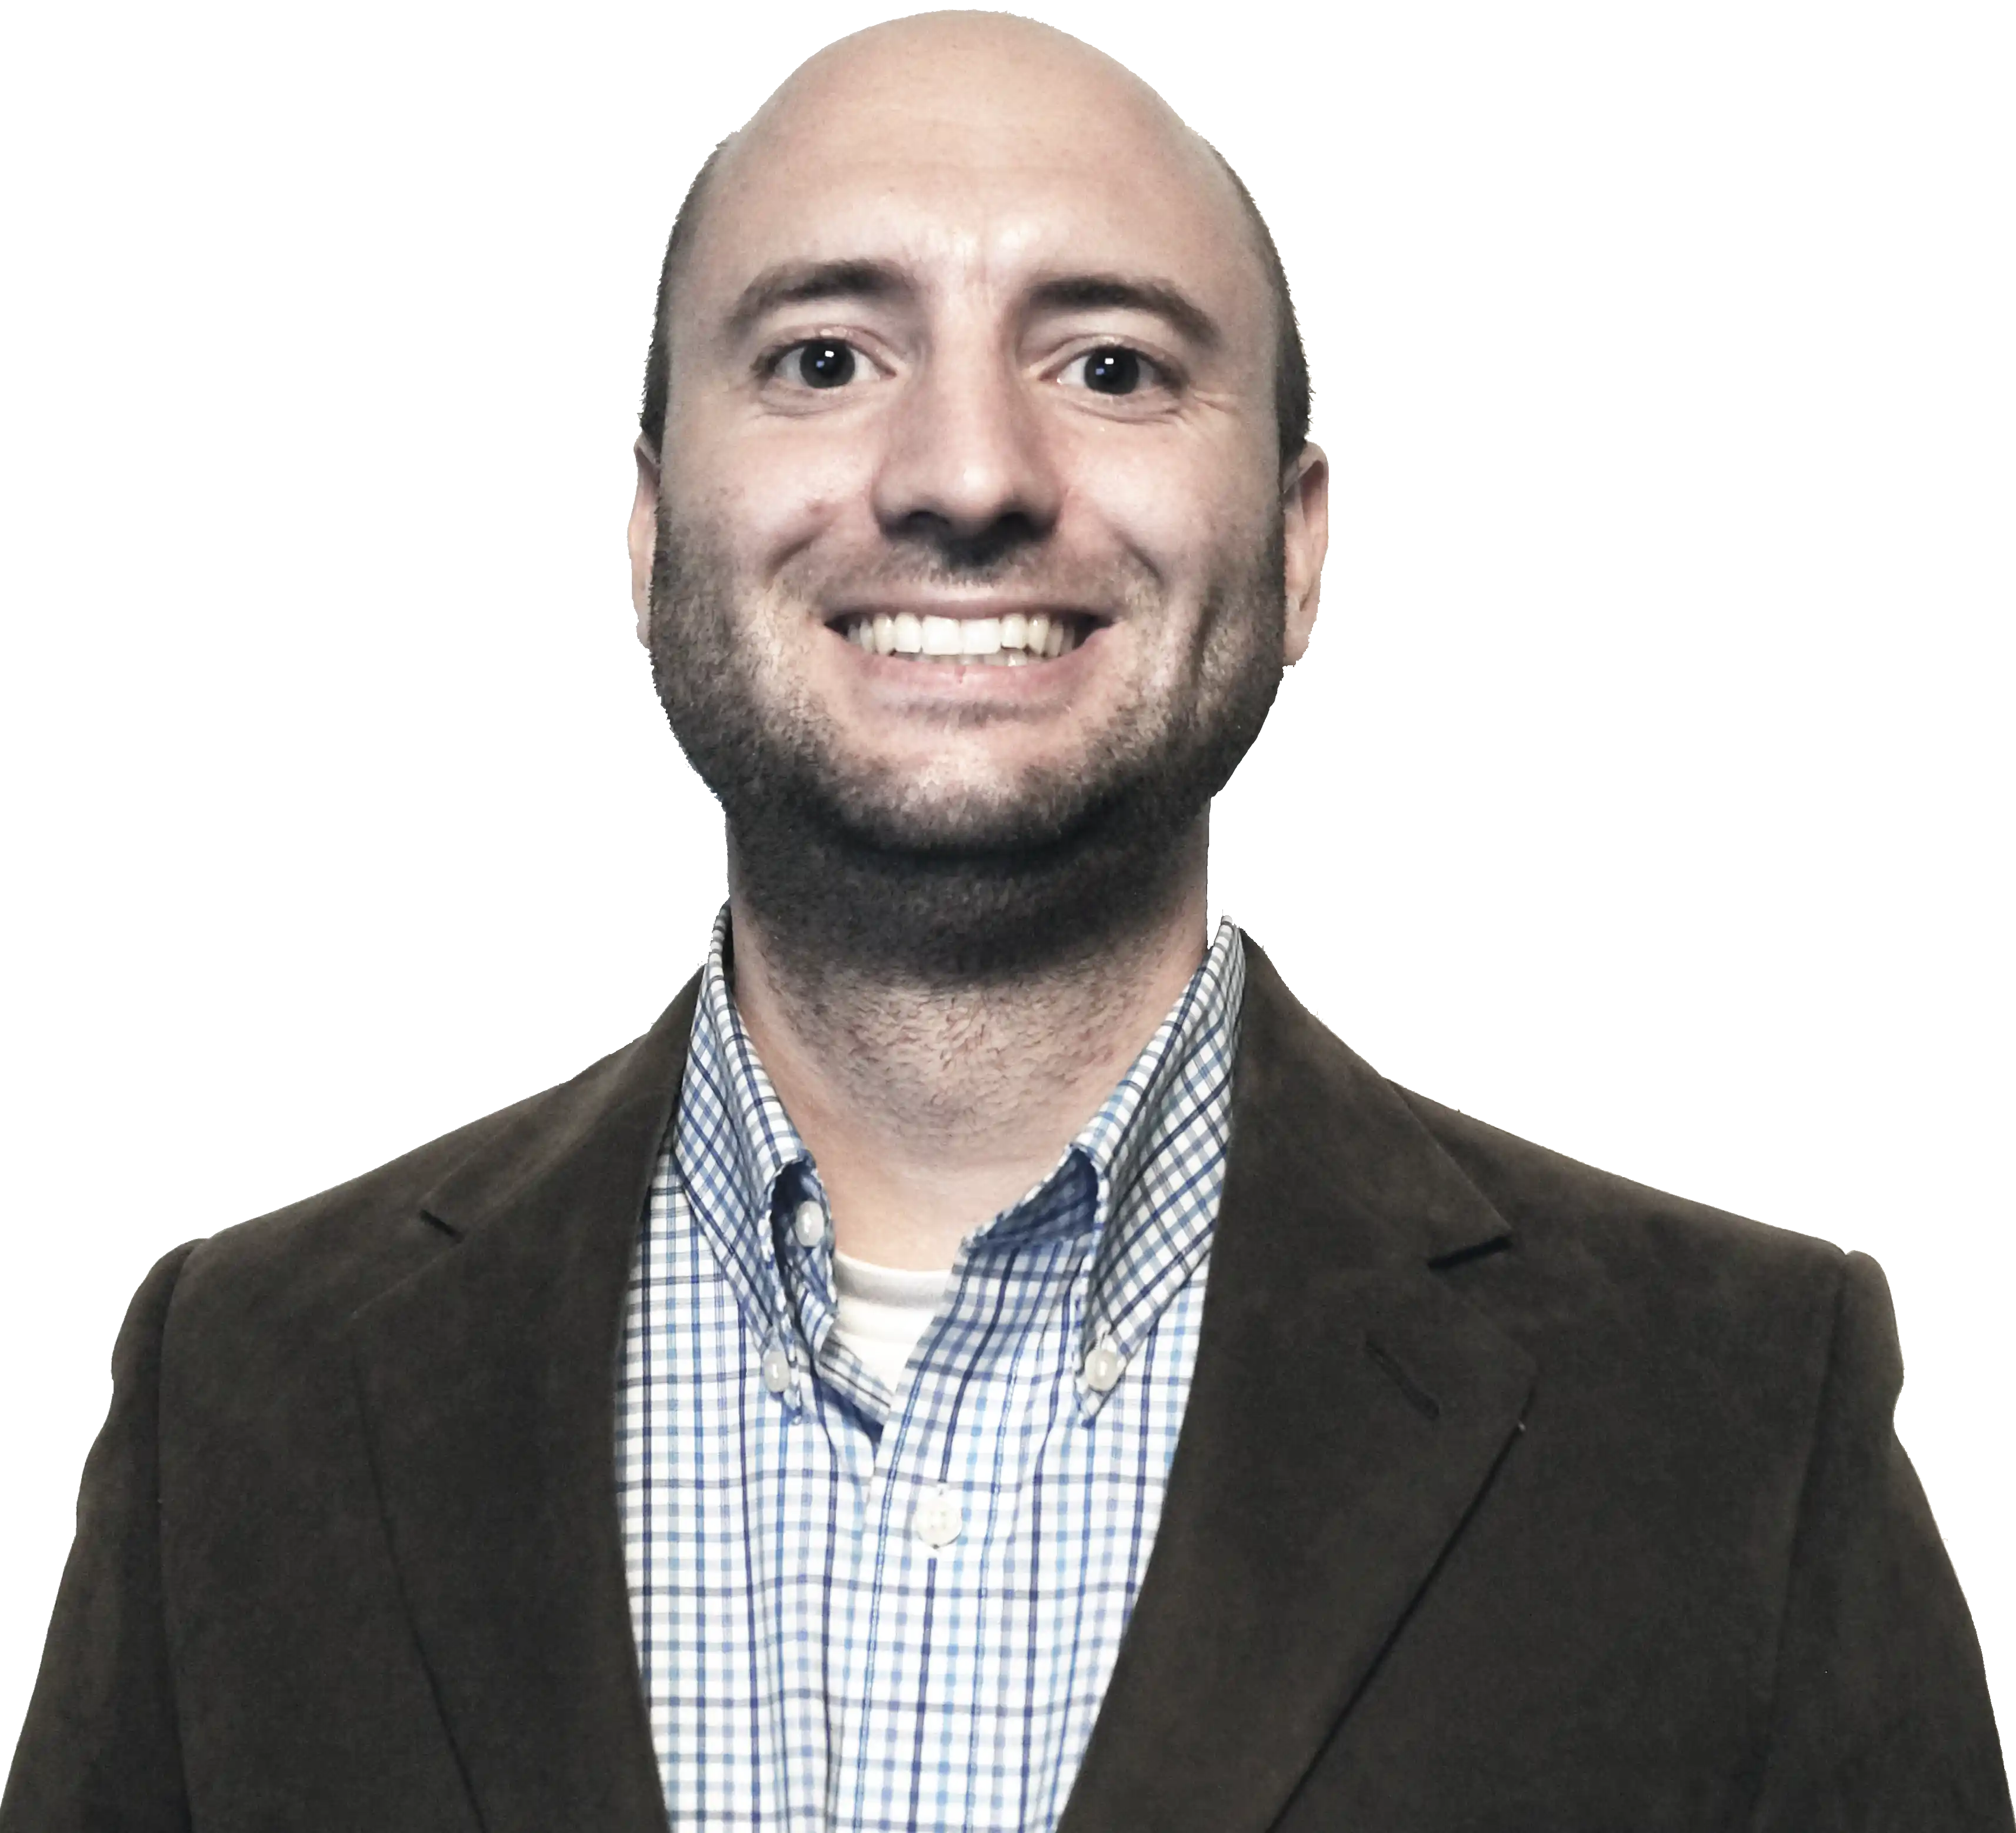
dylan evans · founder
// founder
After more than a decade in traditional cybersecurity across financial services, retail, and manufacturing, Dylan saw the same pattern repeat: firms buying more security tools, spending more money, and still remaining vulnerable to real-world theft.
He started Simple Salt to fix that. Dylan is a frequent speaker on crime prevention, risk modeling, and organizational effectiveness.
He also writes at Salty on Security, a publication of opinions about security, management strategy, and organizational culture. The thesis: security is misunderstood — it’s not as complicated as it seems, and the practices that make organizations excellent tend to also generate strong security.
// why simple salt
Most security consulting firms get a cut of the tools they convince you to buy. We don't. You won't get a garbage product recommendation because it nets us 6 points in margin.
Many consulting firms scare clients with long lists of bad practices to ensure future business. We don't. If you're doing great, we don't manufacture findings.
Many engagements end with arguing between an in-house team and the consultants over a report. We avoid that by sticking with leaders who actually want the unvarnished truth.
A proprietary method to quickly and rigorously assess practical security risk in small and medium businesses — same rigor as Big 4, substantially lower cost.
You get honest, useful advice. The unvarnished truth. And a partner whose only incentive is your safety — not someone else’s margin.
// get in touch
A 30-minute conversation is enough to know whether we can help.